
IML - Radare2 Reverse Engineering: Ep.2 – Windows Binary Part 2
Radare2 Reverse Engineering Ep.2 - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
IML - Radare2 Reverse Engineering: Ep.2 – Windows Binary Part 2#
- We can read all the strings in the binary with:
izz

or to be more precise - we can do:
izz~password

And we get the password:
the_password_tokenNow if we take the address of the password - we can print out a block starting at that position:
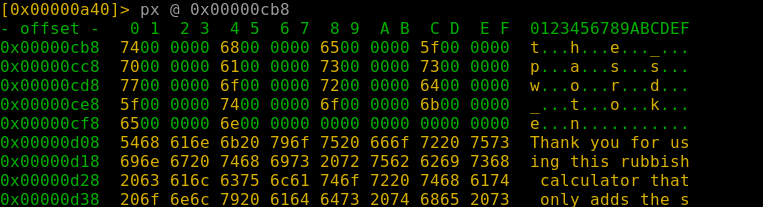
And we get the address of the 7th character
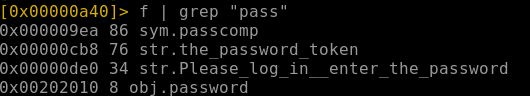
- To get the password compare function we can do:
f | grep "pass"
Related articles
IML - Offensive Cyber Range: Artica Shipping Company
Offensive Cyber Range Artica Shipping Company - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
- ftp
- nmap
- privilege escalation
- python
- rce
IML - Kerberos: Ep.13 – Demonstrate your skills
Kerberos Ep.13 – Demonstrate your skills - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
- hashcat
- john the ripper
- kerberos
- mimikatz
- powershell
IML - Kerberos: Ep.12 – Active Directory Certificate Services
Kerberos Ep.12 – Active Directory Certificate Services - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
- kerberos
- powershell
- privilege escalation
- rce
- windows